
“Compliance should be part of your business strategy, not a side project. We align compliance to business objectives, not the other way around. Risk isn’t about checklists. It should be about helping teams understand what matters, why it matters, and how to implement compliance in a way that fits their organization.”
Enterprise risk management is going through a quiet reset. Many organizations are realizing that the way they’ve handled risk for years—periodic assessments, static templates, and tools that live in silos, simply doesn’t hold up anymore. It looks fine in reports. It checks boxes. But when audits arrive or regulations shift, the cracks show. That’s the gap C2C SmartCompliance steps into, not with another shiny platform, but with a different way of thinking about risk altogether.
At its core, C2C SmartCompliance starts from a belief many companies say they follow but rarely apply in practice: compliance should support the business, not sit beside it. Too often, risk assessment becomes a technical exercise owned by a small group, disconnected from how teams actually work. The result is a risk function that exists on paper but struggles in execution. C2C pushes back on that model. The company aligns compliance to business objectives, not the other way around, and treats risk as something people across the organization need to understand, not just report on.
That philosophy matters because many organizations have already invested heavily in ERM and GRC platforms that promise automation and intelligence. In reality, those tools often become difficult to configure and harder to maintain. They look impressive during demos, but once implemented, teams struggle to use them consistently. The real issue is not the lack of features. It’s the lack of logic. Without meaningful structure, risk data becomes fragmented. Evidence gets scattered. Scoring varies by team. Audits turn into cleanup exercises.
This is where MyRiskAssessor changes the conversation. The platform was built to bring structure to risk work without forcing organizations into rigid templates. It creates a single source of truth by removing disconnected standards, inconsistent scoring, and duplicated effort. Risk assessments become repeatable. Evidence stays in one place. Audit readiness stops being a last-minute scramble and becomes part of how the organization operates day to day. The tool feels practical because it is designed around how risk work actually happens, not how it looks in theory.
But C2C has never positioned MyRiskAssessor as a standalone solution. The platform supports a broader approach that combines technology with deep consulting support. C2C works closely with organizations to define and strengthen their risk, compliance, and security programs. That work often includes designing risk operating models, running maturity assessments, and building realistic roadmaps that teams can actually follow. Framework alignment is a big part of this, whether that means ISO 27001:2022, NIS2, DORA, AI governance, or a mix of requirements that cut across industries and regions.
What stands out in C2C’s consulting work is the focus on integration. Cyber risk doesn’t live in isolation. Neither does privacy, AI, third-party, or operational risk. C2C helps clients move away from fragmented efforts toward a single, cross-discipline risk strategy, all powered by the same underlying logic. Controls get rationalized. Gaps become visible. Teams finally speak the same language when they talk about risk.
The company’s B-GRC framework brings this thinking together in a way that feels grounded rather than theoretical. It starts with the business. It maps requirements once and uses them across the organization. It treats compliance as something that must live in daily operations, not just in policies. And it assumes that compliance is never finished, which means the framework needs to evolve as the business and regulations change. That mindset shows up in both the product and the way C2C works with clients.
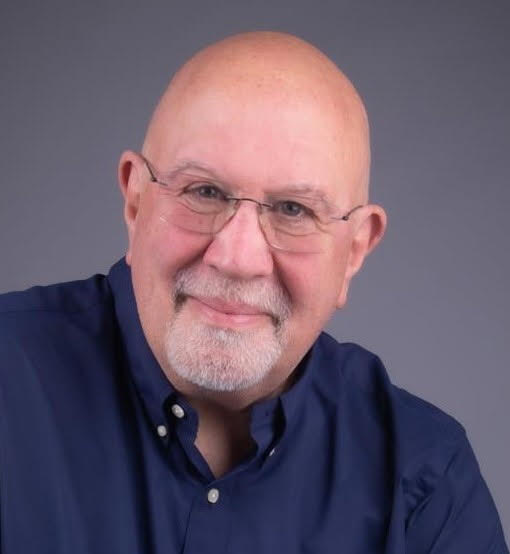
Steve Crutchley, Founder and CEO, puts it simply: “Compliance should be part of your business strategy, not a side project. We align compliance to business objectives, not the other way around. Risk isn’t about checklists. It should be about helping teams understand what matters, why it matters, and how to implement compliance in a way that fits their organization.”
That approach has led to measurable results. One internal law firm operating across multiple jurisdictions had invested in several well-known ERM and GRC tools. Despite that spend, its risk posture remained unclear and inconsistent. There were no shared risk models. No unified scoring logic. Cyber, privacy, and operational risks lived in separate worlds. Control mapping barely existed. C2C implemented MyRiskAssessor with its Unified Risk Logic Layer and replaced five disconnected processes with a single risk engine. Risk registers were consolidated. Scoring models were standardized. Threats, vulnerabilities, and controls finally connected in a way that made sense. The firm moved from confusion to clarity without adding more tools to the stack.
Looking ahead, C2C SmartCompliance is entering a strong growth phase. As organizations move away from siloed risk platforms and toward integrated, intelligence-driven approaches, the company is expanding its footprint, developing new capabilities, and forming strategic alliances to extend its reach. The direction is clear. Risk management needs to work in real environments, with real people, under real pressure.
C2C’s value lies in that realism. It combines tools with guidance. Strategy with execution. Structure with flexibility. Everything it delivers is designed to be used, not just documented. Policies, risks, mappings, and controls are built so teams know exactly what to do and why it matters. And that’s what separates C2C SmartCompliance from many Enterprise Risk Management companies today. It doesn’t just help organizations look compliant. It helps them operate that way.