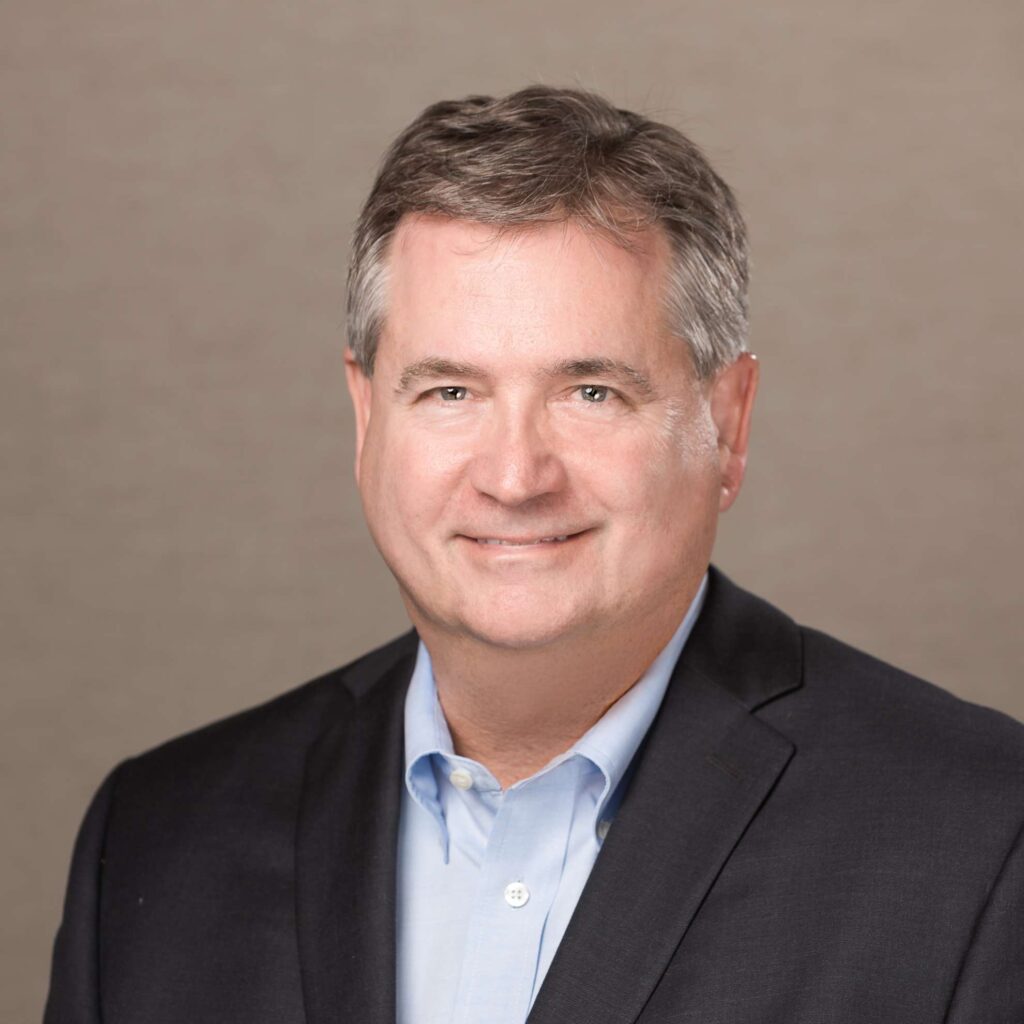

“Leading organizations are no longer asking only, ‘How do we secure every payment system?’ They’re also asking, ‘How do we devalue the data itself, so there’s less to steal and less to protect?’ That shift changes how enterprises approach cybersecurity, compliance, digital transformation, and innovation,” says John Perry, Chief Executive Officer of Bluefin.
Payment security used to sit mainly with IT and compliance teams. Today, it reaches much further. A payment can begin in a store, move through an ecommerce platform, connect with a mobile app, pass through a cloud service, and rely on several third-party providers before the transaction is complete. Newer models, including embedded payments and AI-enabled commerce, add even more connections. Every connection creates another place where sensitive payment and personal data could be exposed.
That is why payment security has become an enterprise architecture issue. Companies still need to meet PCI requirements, of course. But they also need to think about how payment data moves through the business, where it lives, who can access it, and how easily the organization can change its systems without creating new risk.
Bluefin has built its business around that challenge. Founded in 2007 and headquartered in Atlanta, Georgia, the company helps organizations reduce sensitive data exposure across the payment lifecycle. Its platform brings together PCI-validated Point-to-Point Encryption (P2PE), vaultless format-preserving tokenization, payment orchestration, and a processor-independent architecture. The goal is to protect payment data while giving enterprises room to modernize.
Traditional payment security often focused on individual applications, terminals, networks, or cardholder data environments. That approach worked better when payment systems were smaller and more contained. It becomes harder to manage when a business adds cloud applications, mobile channels, connected devices, processors, software providers, and technology partners.
Bluefin starts with a different question. Instead of trying to secure every system on its own, how can an organization reduce the amount of sensitive payment data moving through those systems in the first place?
Its PCI-validated P2PE technology protects payment information at the point of interaction. Vaultless, format-preserving tokenization then replaces sensitive values with secure alternatives that business systems can still use. That matters because companies often need payment data for reporting, customer service, recurring billing, fraud controls, and other operations. They need the data to remain useful without keeping the original sensitive values everywhere.
Payment orchestration adds another layer of flexibility. It helps enterprises manage payment flows across processors and systems without tying the entire environment to one provider. This can simplify compliance, reduce operational risk, and make it easier to add new channels, markets, partners, or technologies.
Bluefin’s processor-independent approach is especially important for large organizations. Most enterprises already have major investments in processors, acquirers, devices, software platforms, and industry applications. Replacing those systems just to adopt a new security model can cost a great deal and create unnecessary disruption.
Bluefin designs its platform to work with existing payment ecosystems. The company works with enterprises, software providers, processors, acquirers, device manufacturers, and other technology partners to integrate encryption, tokenization, and orchestration into current environments. Customers can modernize at their own pace while keeping the systems and relationships that still serve them well.
That partner-focused model also shapes the customer experience. Bluefin does not treat payment security as a one-time installation. Its teams look at how payment data moves through the organization, along with business goals, compliance needs, current infrastructure, and future plans. The work continues as customers enter new markets, integrate acquisitions, add payment methods, or adopt new technology.
One Fortune 500 global retailer shows why this broader view matters. The company had built separate systems for in-store, ecommerce, and mobile commerce. Encryption and tokenization existed in parts of the environment, but different systems and providers handled them in different ways. Payment data became fragmented. Customer activity was harder to connect. Reconciliation took more effort, and adding a new processor or technology could create another round of integration work.
Bluefin helped the retailer rethink the movement of payment data across the enterprise. PCI-validated P2PE protected information at the point of interaction, while vaultless, format-preserving tokens created a consistent way to use payment data across business systems. The processor-independent architecture gave the retailer more choice without forcing a major operational overhaul.
The outcome included less sensitive data exposure, simpler PCI compliance, better reconciliation across channels, and a stronger base for future customer experiences. It also points to a larger lesson. Payment challenges rarely disappear when a company adds one more security tool. The real gains come from connecting security capabilities through a clear, data-focused architecture.
Commerce will keep changing. Artificial intelligence, embedded payments, cloud-native applications, connected devices, and larger partner networks are creating new ways to start and process transactions. Payment data may move through systems that did not exist when many current security models were designed.
“Leading organizations are no longer asking only, ‘How do we secure every payment system?’ They’re also asking, ‘How do we devalue the data itself, so there’s less to steal and less to protect?’ That shift changes how enterprises approach cybersecurity, compliance, digital transformation, and innovation,” says John Perry, Chief Executive Officer of Bluefin.
Bluefin is preparing for that shift by continuing to build infrastructure that protects data wherever commerce takes place. The company plans to expand its ability to orchestrate payment data across complex environments while maintaining processor independence, interoperability, and flexibility. Its partnerships with software providers, processors, financial institutions, device manufacturers, and other technology companies will remain central to that work.
The idea behind the strategy is SECURITY. Security should sit inside the foundation of payment infrastructure, not appear as a separate layer added to every application. When companies reduce the amount of sensitive data they store and share, they can protect information without slowing down innovation.
Bluefin’s approach reflects a wider change in enterprise thinking. The question is no longer only how to secure each payment system. Companies are also asking how to reduce sensitive payment data exposure across the entire business.
That makes payment security part of a much larger conversation involving cybersecurity, compliance, digital transformation, operational resilience, and growth. Bluefin brings those concerns together through a model that combines strong data protection with openness and choice.
With nearly two decades of experience, a processor-independent architecture, and capabilities spanning P2PE, vaultless tokenization, and payment orchestration, Bluefin is building payment infrastructure that can change with the market. Its clients include the University of California System, Springbrook Software, Children’s Healthcare of Atlanta, Costco Canada, and Dover Fueling Systems. The company has also received Cybersecurity Breakthrough Awards in 2025 and 2021, Fortress Cybersecurity Awards in 2025, 2024, and 2022, and FinTech Breakthrough Awards in 2024 and 2021.
As commerce becomes more connected, payment infrastructure cannot stand still. Bluefin puts data protection at the center while preserving the flexibility enterprises need to grow. That creates a payment environment built for today’s security demands and ready for the technologies, partnerships, and customer experiences shaping the next stage of commerce.